When the AI agent becomes an employee: an identity problem

For every human identity registered in corporate systems, there are between 45 and 90 non-human identities operating in the same environments, according to data presented by IBM during Think 2026. These are service accounts, API keys, authentication tokens and, increasingly, AI agents that access CRMs, ERPs, databases and mailboxes with the autonomy to make decisions without human intervention.
The ratio isn't new, but what has changed in recent months is qualitative: AI agents aren't passive credentials. They reason, plan, execute sequences of actions across dozens of systems, and can request new permissions at runtime. And most companies' identity and access management infrastructure was designed for a world in which only people logged in.
In a survey of CISOs by IANS Research, identity assurance for an AI world was ranked as the second-highest priority for this year, scoring 4.46 out of 5, behind only the use of AI within security teams themselves. One of the world's largest technology consultancies included adapting identity and access management for AI agents among the top six cybersecurity trends for 2026, warning that failure to solve the problem will lead to an increase in access-related security incidents as autonomous agents become more prevalent.
What makes this issue particularly difficult is that existing IAM systems were built on assumptions that don't apply to autonomous agents. People log in at predictable times, maintain sessions of limited duration, go through periodic access reviews, and can be subjected to multifactor authentication.
AI agents operate 24 hours a day, at machine speed, without behavioral patterns that can serve as a baseline for anomaly detection, and they cannot respond to an MFA challenge. IBM found that 92% of companies don't trust their own legacy IAM tools to manage the risks associated with non-human identities and AI agents. This isn't an incremental limitation: it's a structural mismatch between the security architecture in place and the operational reality companies are creating by adopting autonomous agents.
Proliferation of autonomous agents
Deloitte, in its 2026 State of AI in the Enterprise report, found that worker access to AI tools grew 50% in 2025 alone, but only one in five companies has a mature governance model to oversee that use. On the agent side, proliferation is even more intense. Each newly deployed agent can generate multiple derived identities, access tokens, and connections to external APIs. A single customer service agent configured to resolve tickets can, in a routine operation, spawn hundreds of sub-agents, each with its own credentials and access scopes. If one of these agents starts issuing refunds outside of policy or accessing customer data without authorization, the question that emerges is simple but frequently unanswered: who configured this agent, what permissions did it receive, and who is responsible for what happened?
A 2026 CSA analysis on token proliferation found that more than 16% of companies don't even track the creation of identities associated with AI agents, meaning basic inventory simply doesn't exist.
Service credentials aren't the same thing
Traditional service accounts perform predefined tasks in deterministic flows. AI agents, by definition, act probabilistically: they interpret context, decide on sequences of action, and can request access to resources their creators never anticipated. A whitepaper published by the Cloud Security Alliance in 2026 described this dynamic as autonomous credential acquisition at runtime, something no previous generation of non-human identities was prepared for.
The credential an agent holds isn't just a passive key, but the primary identity of an actor capable of chaining actions across multiple systems with results that can be unpredictable.
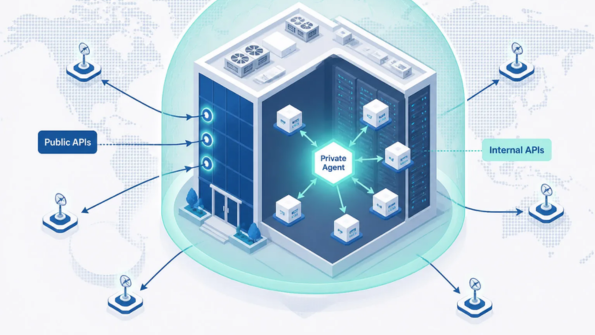
The Zero Trust concept, widely adopted to protect human access, needs to be natively extended to non-human identities and AI agents. This means treating each agent as a first-class entity within the identity system, with dynamic provisioning that creates and retires identities per task, policy-based authorization verified at every invocation, full traceability of each action tied to an auditable delegation chain, and workflow isolation to limit the blast radius in the event of a compromise.
Some analysts already use the term “guardian agents”, supervisory agents whose function is to monitor whether other agents are operating within defined limits, as a necessary layer of governance.
Companies deploying AI agents without first solving the identity issue are building automation on foundations that weren't designed to support it. The next major corporate security failure will likely come not from a sophisticated external attacker, but from an AI agent with excessive permissions that nobody remembers configuring, accessing data nobody authorized, on a system nobody knew was connected.
Translated from the Brazilian Portuguese original · Read the original